Vendor due diligence in insurance is part of regulated risk management because outsourced operations carry the insurer’s regulatory exposure. And the financial stakes of getting due diligence right are high. For instance, IBM’s 2025 report put the average global data breach cost at $4.44 million. Fraud is also costly, with the FBI estimating that insurance fraud costs the average US household between $400 and $ 700 in additional premiums every year.
That is why an outsourcing vendor evaluation checklist matters. It gives insurance companies a repeatable way to assess operations partners before outsourcing. This article walks through the core domains to review before signing an insurance operations partner.
What is a vendor evaluation checklist?
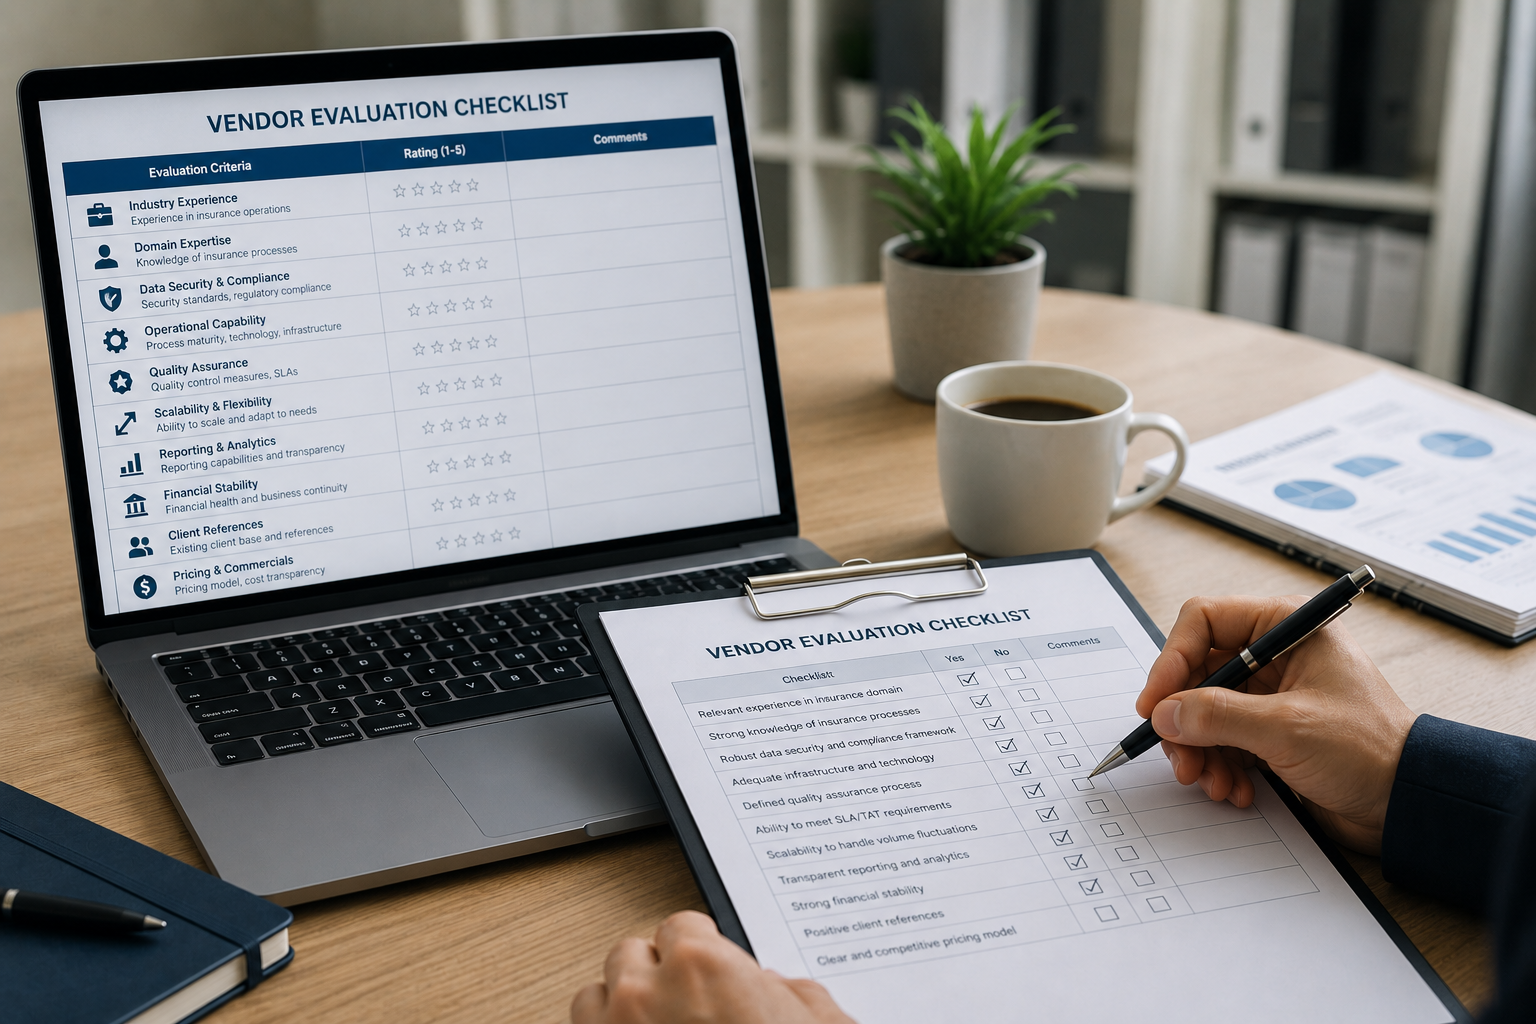
A vendor evaluation checklist is a due diligence tool used to assess whether an outsourcing partner can safely, consistently, and within the buyer’s oversight needs handle a defined function. It helps insurance companies compare vendors across security, regulatory, process, financial, and contract factors.
Having understood what a vendor evaluation checklist is, let’s quickly get into the various checklists that insurers should look at when evaluating outsourcing partners:
Domain 1: Security certifications and evidence
Security documentation should be the first domain reviewed. Insurance outsourcing partners handle sensitive files, so claims about safety need proof before contract signing. A strong insurance operations partner should provide a document pack early in the review. This pack helps the buyer assess whether the partner has formal controls, tested processes, and external reviews. Ask for the following items during due diligence:
- SOC 2 Type II report or ISO 27001 certificate
- ISO 9001 certificate where process quality is relevant
- Audited financial statements
- Business continuity plan
- Disaster recovery plan
- Proof of cyber insurance
- Data processing agreement
- Privacy policy
- Incident response policy
- Access control policy
- Security awareness training records
- Client references from insurers, MGAs, or agencies
- Sample reporting format
- Sample SLA dashboard
Another important thing to keep in mind is to look beyond the certification. SOC 2 Type II and ISO 27001 both signal a control environment. The buyer still needs to verify what the certificate or report covers. Ask these questions before accepting any security certificate:
- Which legal entity holds the certificate?
- Which office or delivery center falls within scope?
- Which service is covered?
- Which systems are covered?
- What audit period does the report cover?
- Were any control exceptions found?
- How were exceptions addressed?
- Does the report cover the work being outsourced?
- Does the report cover subcontractors?
- Does the report cover remote staff access?
Domain 2: Data handling and access controls
Insurance data has high sensitivity. Vendor teams handle policyholder PII, claims records, health-related data, financial records, loss runs, policy forms, payment details, and broker communication. Hence, you should focus on how the vendor receives, stores, accesses, uses, retains, and returns data. For higher-risk work, buyers should ask detailed questions about identity, device, network, and system controls. Use the checklist below during the access review.
| Area to review | What to verify | Why it matters |
| Least privilege | Staff get access only to required systems | Limits exposure if credentials are misused |
| MFA | Users need more than a password | Reduces account takeover risk |
| Device security | Devices have encryption and endpoint tools | Protects workstations handling client data |
| Vulnerability management | Systems get tested and patched | Reduces known security gaps |
| Logging | System activity is recorded | Creates a review trail after incidents |
| Backups | Data has tested backup routines | Protects work during system outages |
| Data retention | Data deletion rules are defined | Reduces unnecessary stored data |
| Incident response | Security events have response steps | Improves speed during an event |
Domain 3: Regulatory and compliance fit
A vendor that works in a variety of industries but not in insurance can still be a poor fit for insurance. Insurance work involves state-based rules, privacy duties, carrier requirements, claims-handling expectations, and health data obligations. For insurance operations, review the following areas.
- State-based insurance data rules
- NAIC data security expectations
- HIPAA requirements where health data is handled
- GLBA-related privacy duties
- Claims file handling rules
- Records retention rules
- Broker and agency data handling requirements
- Carrier system access rules
- State forms and disclosure workflows
- Audit trail needs for outsourced tasks
Domain 4: Operational capability and track record
After security and regulatory fit, the buyer should assess whether the vendor can perform operational tasks well. Insurance operations staff must understand policy records, claims files, endorsements, loss runs, applications, forms, carrier portals, rating inputs, certificates, and renewals. This is where the difference between an insurance KPO and a general BPO becomes important. A general BPO can handle repetitive administrative work. An insurance KPO brings process knowledge tied to insurance workflows. Ask for proof of insurance experience. Request the following items during review:
- Client references from insurers or MGAs
- Experience by product class
- Tenure of insurance-trained staff
- Training materials for insurance workflows
- Sample SOPs for claims, underwriting, audits, or policy servicing
- Error reporting samples
- Quality review samples
- Escalation workflows
- Volume handling history
- Case examples from similar accounts
When considering partners, look for partners like Techsurance that combine domain expertise and trained resources with ISO-certified processes to ensure operational excellence across domains including underwriting, claims processing, risk assessment, hindsighting, and back-office operations.
Domain 5: Cost transparency
Insurance companies should review pricing terms in depth before signing. This helps avoid budget surprises after migration. Here are some cost items that must certainly be reviewed:
| Cost area | What to check | Question to ask |
| Base pricing | Monthly fees or per task rates | What does the base fee include? |
| Volume bands | Price changes as volume rises | What happens when volume spikes? |
| Transition fees | Setup, training, and migration charges | Which startup costs appear in month one? |
| Professional services | Extra process design or reporting work | What hourly rate applies to change work? |
| Reporting | Dashboard and analytics costs | Are reports included in the base fee? |
| System access | Licensing or user charges | Who pays platform access costs? |
| Data transfer | Export or data egress fees | What costs apply when data leaves the system? |
| Escalated service tiers | Premium service charges | Which SLA level changes pricing? |
| Exit costs | Data return and transition charges | What costs apply at contract end? |
Domain 6: Business continuity and exit readiness
A vendor evaluation checklist should also cover disruption planning. You need to know how work continues during outages, staff shortages, office closures, cyber incidents, system downtime, or natural disasters. Business continuity review protects the insurer’s ability to serve brokers, policyholders, and claimants during stressful periods. Ask for a business continuity plan and disaster recovery plan. Use the questions below to test readiness:
- When was the plan last tested?
- Which teams joined the last test?
- What systems were part of the test?
- What recovery time target applies?
- What recovery point target applies?
- Which alternate sites can handle the work?
- How does staff access work during outages?
- How does the vendor contact client teams during incidents?
- What happens to active tasks during system downtime?
- Who approves temporary workarounds?
Exit readiness deserves the same level of review. A strong contract should explain what happens to data, active files, credentials, reports, and knowledge transfer at exit. Ask these exit questions before signing:
- How will data be returned?
- What format will be used?
- How will data deletion be confirmed?
- What happens to active work?
- Who handles transition during exit?
- How long will exit help continue?
- What fees apply during exit?
- How will system access be removed?
- How will client documents be destroyed or archived?
- What reports will be delivered at the end?
Checklist domain vs what to verify
A checklist becomes more useful when each domain has specific verification items. This prevents broad yes-or-no answers from replacing careful review. Here is a way to effectively compare vendors:
| Checklist domain | What to verify | Review owner |
| Security certifications | SOC 2 Type II, ISO 27001, ISO 9001, scope, period, exceptions | Security team |
| Data handling | Access controls, MFA, logging, backups, retention, incident response | IT and privacy team |
| Regulatory fit | State insurance rules, HIPAA where needed, data controls | Legal and risk team |
| Process capability | Insurance workflow experience, SOPs, training, QA samples | Operations leader |
| Track record | References from similar insurers or MGAs | Business sponsor |
| Cost transparency | Base fees, overages, reporting costs, exit fees | Finance team |
| Financial stability | Audited financials, ownership, insurance cover | Finance and legal |
| Business continuity | Tested continuity and recovery plans | Risk team |
| Exit readiness | Data return, deletion proof, work transition, access removal | Legal and operations |
Ongoing monitoring after signing
Vendor due diligence should continue after contract signing. A vendor that passed review 18 months ago can undergo changes, including changes in ownership, the loss of key staff, changes in delivery centers, the addition of subcontractors, a security incident, or alterations to its systems. Ongoing monitoring helps the insurer spot changes early and provides both sides with a planned cadence for review, rather than waiting for a problem.
Set a monitoring cadence based on risk. High-risk vendors need more frequent reviews than vendors handling low-sensitivity work. Here’s a simple monitoring model:
| Review item | Suggested cadence | What to review |
| SLA performance | Monthly | Volumes, turnaround time, error rates |
| Quality review | Monthly or quarterly | QA findings, rework, corrective actions |
| Security certificate status | Annual | Expiry dates, scope changes, exceptions |
| Access review | Quarterly | Active users, permissions, leavers |
| Incident review | Quarterly | Security events, near misses, response time |
| Business review | Quarterly | Staffing, productivity, client escalations |
| Business continuity test | Annual | Test results and action items |
| Financial health check | Annual | Audited statements and insurance cover |
| Contract review | Annual | Scope, pricing, exit terms, change requests |
How Techsurance measures up against this checklist
Techsurance provides insurance operations services across underwriting assistance, claims processing, policy servicing, and back office administration. The key value offering that Techsurance provides is a blend of trained teams, robust processes underpinned by ISO 27001/9001 certification and process management tools that boost efficiency. Here’s how Techsurance measures up against the various evaluation checklists we covered earlier:
| Evaluation area | Techsurance value proposition | Business benefit |
| Insurance domain capability | Teams trained on insurance workflows | Less ramp time for insurance tasks |
| Process execution | Defined workflows for service areas | More consistent work movement |
| QA/QC | Review steps across key tasks | Fewer rework cycles |
| Audits | File review and audit assistance | Better visibility into file quality |
| Back office administration | Scalable task handling | More capacity during volume peaks |
| Reporting | Workflow and performance tracking | Better management visibility |
Conclusion
A thorough outsourcing vendor evaluation checklist protects the insurer’s regulatory position, data, workflow quality, and cost control. It also prevents vendor selection from becoming a price-only decision.
Insurance companies should review security certifications, data access, regulatory fit, process capability, cost transparency, financial stability, business continuity, exit readiness, and post-signing monitoring before choosing an operations partner.
The strongest outsourcing partnerships withstand this level of scrutiny because their processes, documentation, and controls can be reviewed directly. That level of maturity matters when the outsourced work touches policyholders, claims, forms, carrier systems, and financial records.
Techsurance works with insurance businesses that need domain-trained operations teams across a range of insurance operations workflows, including underwriting assistance, claims processing, policy servicing, and back-office administration. To learn more about how our team can add value to your business, get in touch today.
FAQs
What is a vendor evaluation checklist for insurance companies?
A vendor evaluation checklist helps insurance companies assess an outsourcing partner before signing. It covers security, data handling, regulatory fit, process capability, cost terms, financial stability, business continuity, and exit readiness. The goal is to protect the insurer’s oversight position and reduce risk linked to outsourced work.
Why is vendor due diligence important in insurance outsourcing?
Vendor due diligence matters because outsourced functions still expose the insurer. Insurance vendors handle policyholder PII, claims records, forms, financial data, and access to carrier systems. A thorough review helps confirm that the partner can handle these workflows safely and consistently.
What documents should an insurance outsourcing vendor provide?
An insurance outsourcing vendor should provide SOC 2 Type II or ISO 27001 documentation, audited financial statements, business continuity plans, proof of cyber insurance, privacy policies, data processing agreements, incident response policies, and client references. The buyer should review scope, dates, exceptions, and service coverage.
How often should insurers reassess outsourcing vendors?
Insurers should reassess high-risk outsourcing vendors at least once a year. Monthly or quarterly reviews should cover SLA performance, quality, access rights, incidents, and staffing changes. Annual reviews should cover certifications, business continuity tests, financial health, contract terms, and exit readiness.
What is the difference between vendor evaluation and vendor monitoring?
Vendor evaluation happens before signing. It checks whether the vendor is suitable for the work. Vendor monitoring happens after signing. It reviews performance, security status, access, incidents, staff changes, certifications, and service quality throughout the relationship.
What are the biggest risks in insurance outsourcing vendor selection?
The biggest risks include poor data controls, lack of insurance domain knowledge, weak QA, unclear pricing, limited business continuity planning, and poor exit readiness. These issues can lead to rework, service delays, data exposure, audit issues, and higher long-term costs.
